App Building
Application security: a complete guide
Ready to see what Base44 can do for you? Get started →
This guide empowers vibe coders of all skill levels to understand security fundamentals and secure their applications from day one. Whether you're building your first landing page or launching a commercial product, these principles will help you create secure, trustworthy applications.
Vibe Coding is revolutionizing software development by democratizing the app building process, enabling anyone to transform ideas into live applications without traditional coding barriers. As more creators embrace this paradigm, security becomes not just important, but essential.
Try vibe coding out for yourself. Learn how to build an app with AI and see how the best AI app builders can bring your ideas to life.
Base44 includes a built-in security scanner, role-based access control, field-level data permissions, and secrets management, giving every app builder a complete set of security tools without needing a security background.
App security 101
Application security (AppSec) refers to the practices, tools, and processes that protect software applications from threats, unauthorized access, and data exposure. For vibe coders, this means making intentional choices about who can access your app, what data is visible, and how user information is stored and protected.
Base44 is a platform that closes the gap between imagination and execution by turning rough conversational prompts into structured fully functional products.
Whether you're launching your first app or hardening an existing product, this guide provides actionable steps to build secure, trustworthy applications that protect your users' data while avoiding the most common app security mistakes. Here’s what this guide includes:
Security workflow and tools
- When to start thinking about security (and why timing matters)
- How to use Base44's built-in security check to identify vulnerabilities
- Leveraging Safe Vibe Codes for external security scanning
- The iterative security hardening loop for continuous protection
Core security concepts
- App visibility settings and the principle of least privilege
- Authentication and password management best practices
- Role-Based Access Control (RBAC) for permission management
- Row Level Security (RLS) for controlling data access
- Field Level Security (FLS) for granular permissions on mixed data
Real-world examples
- Securing a landing page with contact form
- Protecting an e-commerce product catalog
- Implementing user-specific data isolation in finance apps
- Managing mixed public/private data
Advanced protection
- Backend functions for hiding sensitive logic and code
- Secrets management for API keys and credentials
- Server-side validation and rate limiting
Practical resources
- Pre-launch security checklist
- Common mistakes to avoid
- When to seek expert help
- Next steps for ongoing security
When app security becomes critical
Many app builders begin with experimentation—playing with ideas, testing concepts, and iterating rapidly. During this exploratory phase, security may not be your primary concern. However, recognizing when you transition from prototype to production is crucial for implementing security at the right time.
You must prioritize app security when any of these conditions apply:
Real users are active on your app
- Your app has moved beyond personal testing
- Others are depending on your application's availability and reliability
- User trust becomes a factor in your app's success
Private or sensitive data is stored by your app
- Personally Identifiable Information (PII): names, addresses, phone numbers, emails
- Financial data: payment methods, transaction history, account balances
- Business-sensitive information: proprietary content, internal communications
- Any data that shouldn't be publicly accessible
Why security-first?
Start early, save time. Retrofitting security into an existing application is exponentially more difficult than building it in from the beginning.
Think of security like building foundations, much easier to get right at the start than to fix later.
Base44 is SOC 2 Type II compliant and ISO 27001 certified, meaning the platform has been independently audited and verified to meet rigorous data protection standards. Building on a certified platform means your app's security foundation starts strong before you write a single prompt.
App security getting started
- Built-in security check
- Safe Vibe Codes external security scanner
- The security hardening loop
01. Base44 built-In security check
Base44's integrated security scanner serves as your first line of defense, identifying common vulnerabilities before they become serious problems.
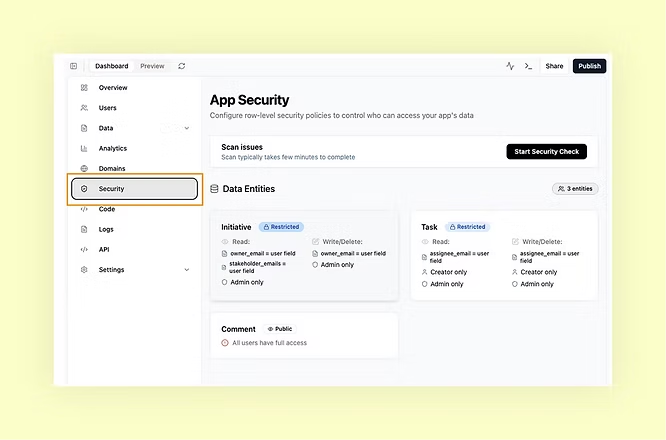
What it detects:
- Exposed sensitive data
- Leaked API keys and secrets
- Misconfigured access controls
- Common security anti-patterns
How to use it:
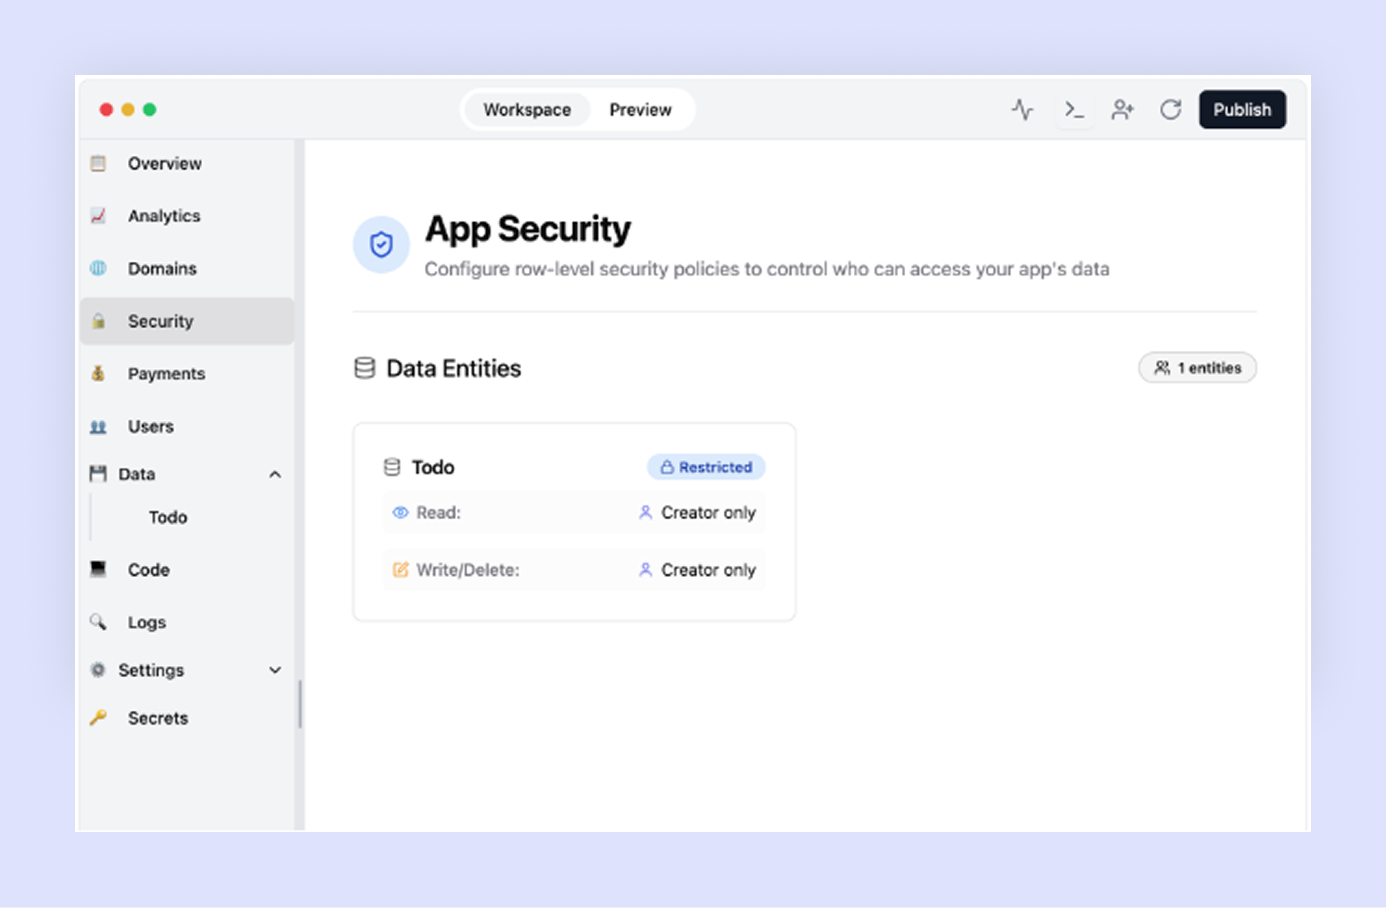
- Access the security check from your Base44 dashboard
- Review flagged issues with contextual explanations
- Apply suggested fixes with one-click remediation where available
02. Safe Vibe Codes external security scanner
Safe Vibe Codes (safevibe.codes) provides an external perspective on your application's security posture, showing exactly what data is accessible to anonymous users on the internet.
Key capabilities:
- External vulnerability scanning
- Data exposure mapping
- Real-time security posture assessment
- Clear severity ratings for discovered issues
How to use it:
- Navigate to safevibe.codes
- Enter your application's URL
- Review the exposure report
- Identify which data shouldn't be public
- Use the findings to guide your security configuration
03. The security hardening loop
Follow this iterative process to systematically secure your application:
- Initial scan: Run Safe Vibe Codes to establish baseline security posture
- Internal check: Execute Base44's built-in security check
- Apply fixes: Implement suggested remediations
- Verify: Re-scan with Safe Vibe Codes to confirm issues are resolved
- Manual review: For remaining exposures, manually configure security settings or consult an expert
Pro tip: As your product evolves, run security scans regularly (weekly or monthly) to catch new vulnerabilities introduced by changes or updates.
App security best practices
- App visibility
- Authentication and password management
- Data access control: RLS and FLS
01. App visibility, your first security layer
Base44's app visibility settings control who can access your application at the broadest level. This is your first and most fundamental security decision.
The principle of least privilege
Always default to the most restrictive setting that allows your app to function. You can always expand access later but you can't un-expose data that's already been leaked.
Visibility Levels
Private
- Only visible to you and explicitly invited users
- Best for: Internal tools, admin dashboards, development/staging environments
- Security benefit: Smallest attack surface, controlled user base
Public with login required
- Anyone can discover your app, but must authenticate to use it
- Best for: SaaS applications, member portals, social platforms
- Security benefit: User accountability, controlled access to features
Public without login
- Fully accessible to anyone on the internet
- Best for: Marketing sites, public content, e-commerce storefronts
- Security benefit: Maximum reach (but requires careful data protection)
Decision framework:
- Who is your intended audience?
- Does your app handle user-specific data?
- Do you need to track who does what?
- Is there value in keeping the app discoverable to search engines?
Read the full guide to documentation management.
02. Authentication and Password Management
Built-In authentication
Base44 handles authentication and password security automatically, implementing industry best practices:
- Secure password hashing
- Protection against common attacks
- Session management
- Password reset flows
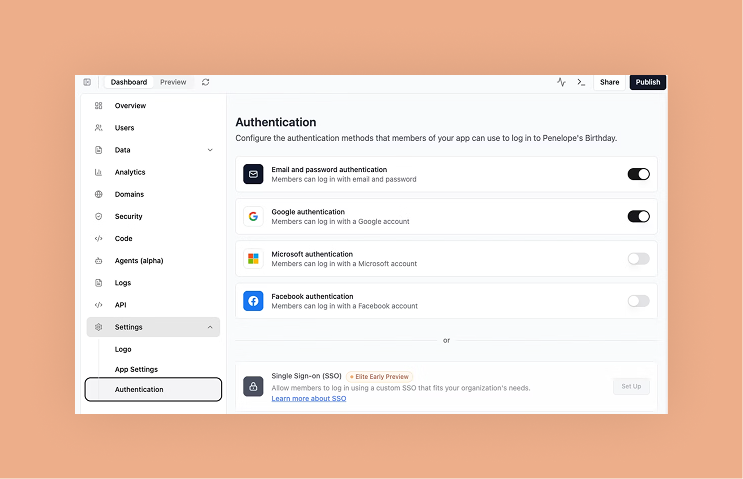
Critical tip: Never build your own authentication system.
Custom login mechanisms frequently contain security vulnerabilities. Use Base44's built-in authentication instead.
Role-based access Control (RBAC)
For administrative access or permission tiers, use Base44's roles feature:
- Assign roles to users (e.g., admin, user)
- Reference roles in RLS/FLS rules
- Manage role assignments through the dashboard
Anti-pattern to avoid: Creating custom "admin password" fields or building your own role system. These approaches bypass Base44's security features and introduce vulnerabilities.
Read the complete guide to access management.
03. Data access control: RLS
Understanding Base44's data model
In Base44, your application data is organized in tables—similar to spreadsheets. Each table represents one type of entity (users, products, orders) with fields (columns) storing specific attributes (name, price, status).
Every table has granular security settings that control data access at multiple levels.
Row Level Security (RLS)
RLS controls access to entire records (rows) in a table. You configure four distinct permission types:
READ: Who can view existing records
- Controls data visibility
- Affects API queries, list views, detail pages
- Example: "Only show users their own orders"
WRITE: Who can create new records
- Controls data insertion
- Affects form submissions, API POST requests
- Example: "Anyone can submit a contact form"
UPDATE: Who can modify existing records
- Controls data changes
- Affects edit forms, API PATCH/PUT requests
- Example: "Users can only edit their own profile"
DELETE: Who can remove records
- Controls data deletion
- Affects delete actions, API DELETE requests
- Example: "Only admins can delete products"
Application security in action (with practical examples)
Let's explore real-world scenarios with complete security configurations.
Example 1: Landing page with contact form
The scenario
You're creating a landing page for your business with a contact form collecting visitor information (names, emails, phone numbers).
Base44 prompt
"Create a landing page with a contact form"
Initial state (Insecure)
- App Visibility: Public without login (correct)
- Contact table: Fully accessible (WRONG!)
By default, anyone can read all submitted contact information—a serious privacy violation.
Safe Vibe Codes detection
Running the app through Safe Vibe Codes reveals:
- Contact form data exposed to anonymous users
- High severity: PII accessible without authentication
- Recommendation: Implement access controls
Security configuration
App Visibility: Public without login
- Visitors must be able to access the form without barriers
Contact Table RLS:
READ: Admin only
Rationale: Only you should see contact submissions
WRITE: No restrictions
Rationale: Anyone can submit the form
UPDATE: Admin only
Rationale: Only you should modify submissions
DELETE: Admin only
Rationale: Only you should remove submissions
Verification
Re-scan with Safe Vibe Codes to confirm the data is no longer exposed.
Example 2: E-commerce store
The scenario
An online store where you manage a product catalog and customers can browse and purchase items.
Base44 Prompt
"Create a t-shirt shop website"
This is a long article and only part of it is shown here. Read the full article on iCARE.